AI & Agentic Security Assurance
Secure AI before it ships to production.
Independent AI security architecture and assurance for organizations that need to identify architectural weaknesses, excessive agent privileges, data exposure, and insecure delivery practices before AI systems create operational, regulatory, or business risk.
Architecture reviews, AI security assessments, authorized attack simulation, CI/CD security, and fractional AI security leadership.
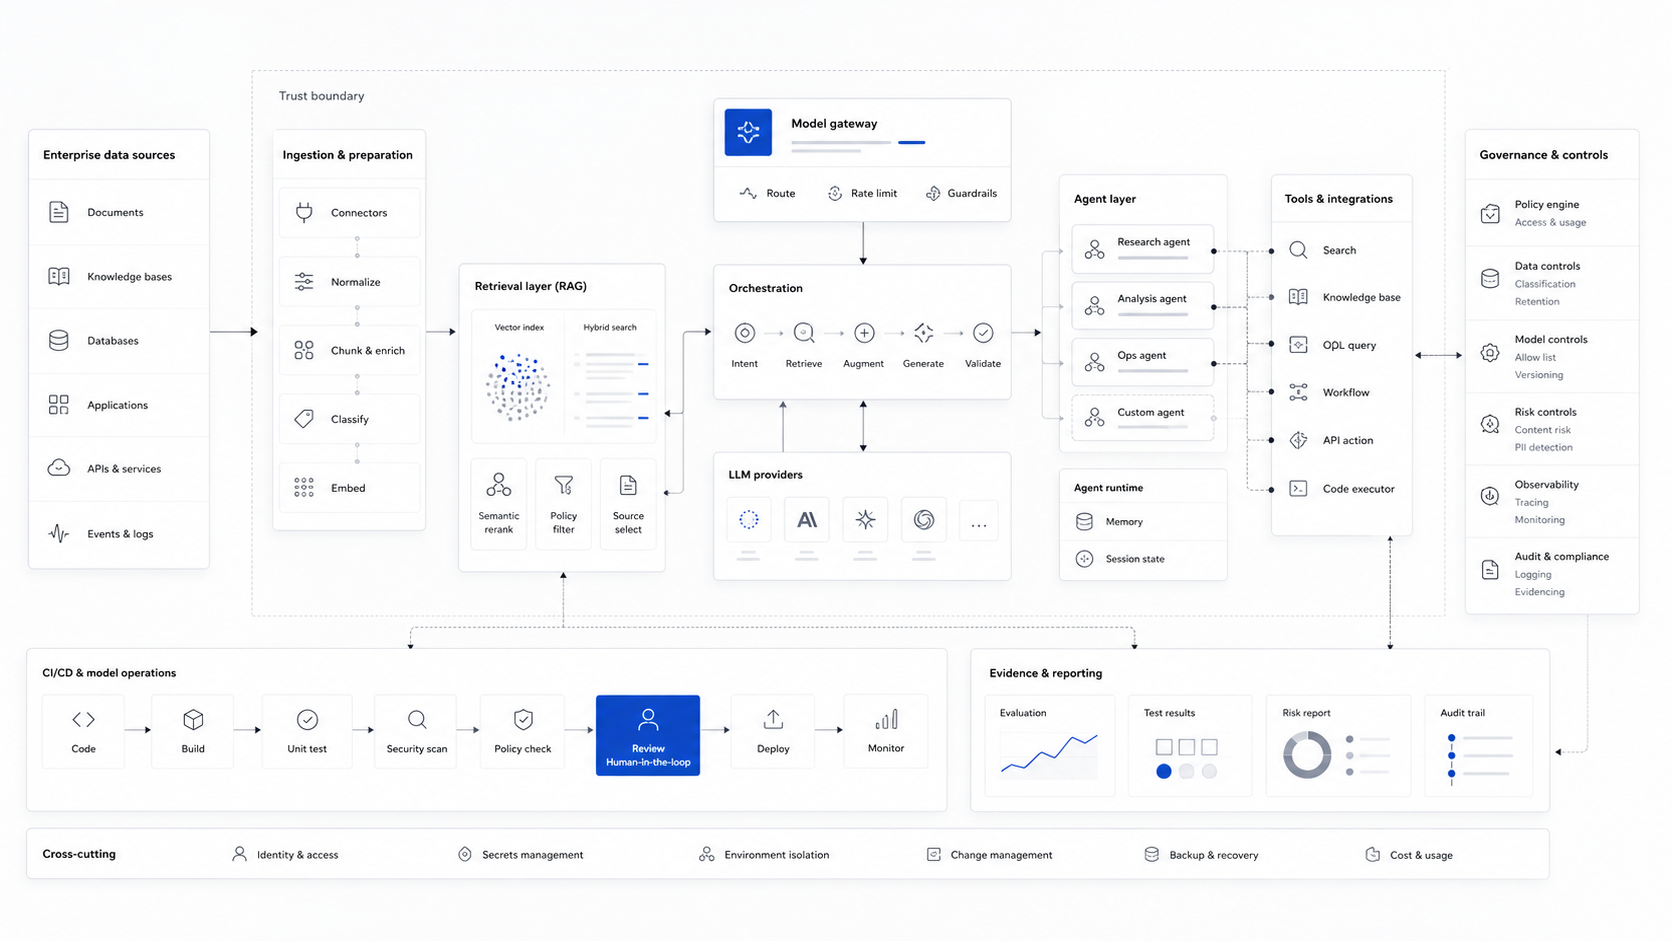
From finding risk to proving controls work.
Assurance-AI is the AI and agentic security assurance platform developed by Assured-AI Security. It runs repeatable adversarial tests and verifies defenses with execution evidence.
- DiscoverMap AI risks, trust boundaries, and attack surface.
- TestRun repeatable adversarial scenarios against authorized systems.
- ProveSeparate unsafe model output from observable security effects.
- ProtectVerify guardrails with retests and enforce results in CI/CD.
AI is moving faster than traditional security review models.
Enterprise AI introduces natural-language attack surfaces, dynamic tool execution, non-human identities, retrieval risk, and new delivery pipelines. Leaders need independent judgment about what could fail, why it matters, and what to fix first.
Prompt injection
Test whether untrusted instructions can override intended behavior, leak data, or trigger unsafe actions.
Overprivileged agents
Simulate tool abuse and privilege misuse paths to validate whether agents can act beyond business need.
Insecure RAG
Assess authorization, source trust, chunk metadata, data leakage, and retrieval manipulation scenarios.
Weak AI CI/CD
Evaluate prompts, models, evaluations, artifacts, secrets, approvals, rollback readiness, and bypass paths.
Focused services for enterprise AI risk.
Each engagement helps clients reduce a specific business or security risk, make clearer decisions, and leave with consultant-reviewed outputs their teams can act on.
Why Independent Review
AI security problems rarely exist in isolation.
They span architecture, identity, data, application behavior, cloud infrastructure, and software delivery. Independent review connects those layers so organizations receive a complete view of risk and a practical path forward.
Probabilistic behavior
Outputs, tool calls, and retrieval paths can vary. Controls need validation under realistic scenarios.
Indirect instructions
Untrusted documents, tickets, websites, and messages can become attacker-controlled prompts.
Agent privilege
Agents need identity, authorization, approval, and logging models that match their authority.
Prompt supply chains
Prompts, policies, evaluations, and model configuration are delivery artifacts that need governance.
A practical methodology for trusted outcomes.
Our assessments combine senior security architecture expertise with structured review methods, repeatable evidence collection, authorized attack simulation, adversarial prompt testing, technical validation, and framework-aligned analysis.
Discover
Clear scope and shared understanding of the business objective, architecture, data, identities, integrations, and deployment model.
Model
Visibility into trust boundaries, attack paths, dependencies, and failure scenarios that could create AI-related risk.
Attack and Validate
Use Assurance-AI to run authorized, repeatable adversarial scenarios that test guardrails, tool permissions, approval paths, and response handling, with evidence of what the system actually did.
Prioritize
A practical view of what matters most based on business impact, exposure, likelihood, and existing controls.
Remediate
An actionable roadmap with recommendations, sequencing, validation steps, and ownership guidance.
Framework mapping when it helps the decision.
Consultant-reviewed findings can be mapped to recognized security and governance frameworks based on client requirements. Mapping does not represent formal certification, and framework names do not imply endorsement.
Example Deliverables
Decision-ready outputs, not vague risk language.
- Consultant-reviewed executive summary
- Evidence-backed technical findings
- Attack simulation findings
- Architecture threat model
- Control gap analysis
- Risk register
- Framework alignment matrix
- Evidence matrix
- Prioritized remediation roadmap
- Validation and retest plan
- Maturity assessment
AI Security Architecture Review Checklist
Prepare for a review with evidence categories for architecture, data flow, identity, RAG, agent permissions, MCP integrations, CI/CD controls, monitoring, and governance.
View the ChecklistBuilt for teams deploying internal AI.
Appropriate for enterprise AI programs, internal chatbots, RAG platforms, AI agents, MCP adoption, AI-enabled CI/CD, regulated data, and governance readiness.
AI platform teams
Validate architecture, data flow, identity, and deployment choices before broad rollout.
Security leaders
Get independent evidence for risk acceptance, remediation planning, and governance review.
Engineering leaders
Secure AI delivery pipelines, agent permissions, and operational guardrails.
Founder-led expertise
Led by an AI security architect with hands-on offensive and defensive experience.
Assured-AI Security is founded by Alejandro Aucestovar, a Principal AI Security Architect with 20 years of cybersecurity experience across AI/LLM security, cloud architecture, application security, DevSecOps, offensive security, and incident response.
Why it matters
Clients get senior-level judgment, practical attack simulation, and evidence-backed recommendations from a specialist focused on AI security assurance.
Insights for AI security leaders.
View InsightsBuilding or deploying AI internally?