About
Independent AI security judgment grounded in architecture and evidence.
Assured-AI Security exists to help organizations adopt AI responsibly by identifying practical security risks in LLM, RAG, agentic AI, MCP, and AI delivery systems before they become operational incidents.
Founder
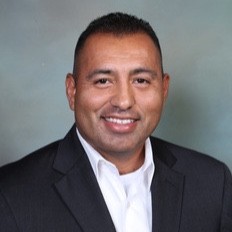
Alejandro Aucestovar, Founder and Principal AI Security Architect
Alejandro brings 20 years of cybersecurity experience spanning AI/LLM security, application security, DevSecOps, multi-cloud architecture, offensive security, incident response, and enterprise risk.
His recent work includes AI/LLM threat modeling, control mapping, guardrail validation, attack simulation, and CI/CD security testing for prompt injection, tool abuse, sensitive-data leakage, insecure model outputs, and policy violations.
Selected credibility
- CISSP, CISM, PMP
- GIAC: GPCS, GWAPT, GPEN, GDSA, GCCC, GCIH, GSEC, GCIA
- AWS Certified Solutions Architect - Associate and AWS Certified Security - Specialty
- M.S. Information Security, SANS Institute of Technology
- Presented at SANS Cloud Security Exchange Summit 2026: Securing AI/LLM Workloads in CI/CD
Company purpose
The practice focuses on specialized AI security architecture and assurance, not broad generic cybersecurity services. Engagements are designed to help leaders make informed decisions about risk, control design, and remediation priority.
Built around practical assurance
Assured-AI Security helps teams determine whether AI systems can be trusted under realistic use, misuse, adversarial prompting, excessive permission, sensitive-data, and deployment-control scenarios.
Engagements are designed to produce decision-ready evidence for security leaders, platform teams, engineering leaders, and executives responsible for approving AI systems.
Professional values
These principles should guide copy, delivery, sales conversations, and client work.
Evidence over hype
Findings should be grounded in scope, artifacts, observed behavior, and clear assumptions.
Secure by design
Review risk early enough that architecture, identity, and data-flow decisions can still change.
Practical remediation
Recommendations should be feasible, prioritized, and tied to measurable risk reduction.
Independence
Advice should remain objective, confidential, transparent, and free from fabricated proof.
Methodology
Discover, model, validate, prioritize, and remediate. The method keeps technical depth connected to executive action.
How engagements stay useful
- Define the business decision the assessment must support
- Map AI data flows, identities, retrieval paths, tools, agents, and deployment controls
- Use authorized adversarial prompts and attack simulation to validate controls
- Prioritize findings by exploitable risk and remediation leverage
- Translate evidence into a practical roadmap leaders can act on
Need an independent review?
Start with a consultation to determine whether architecture review, assessment, CI/CD review, readiness workshop, or fractional support fits best.